
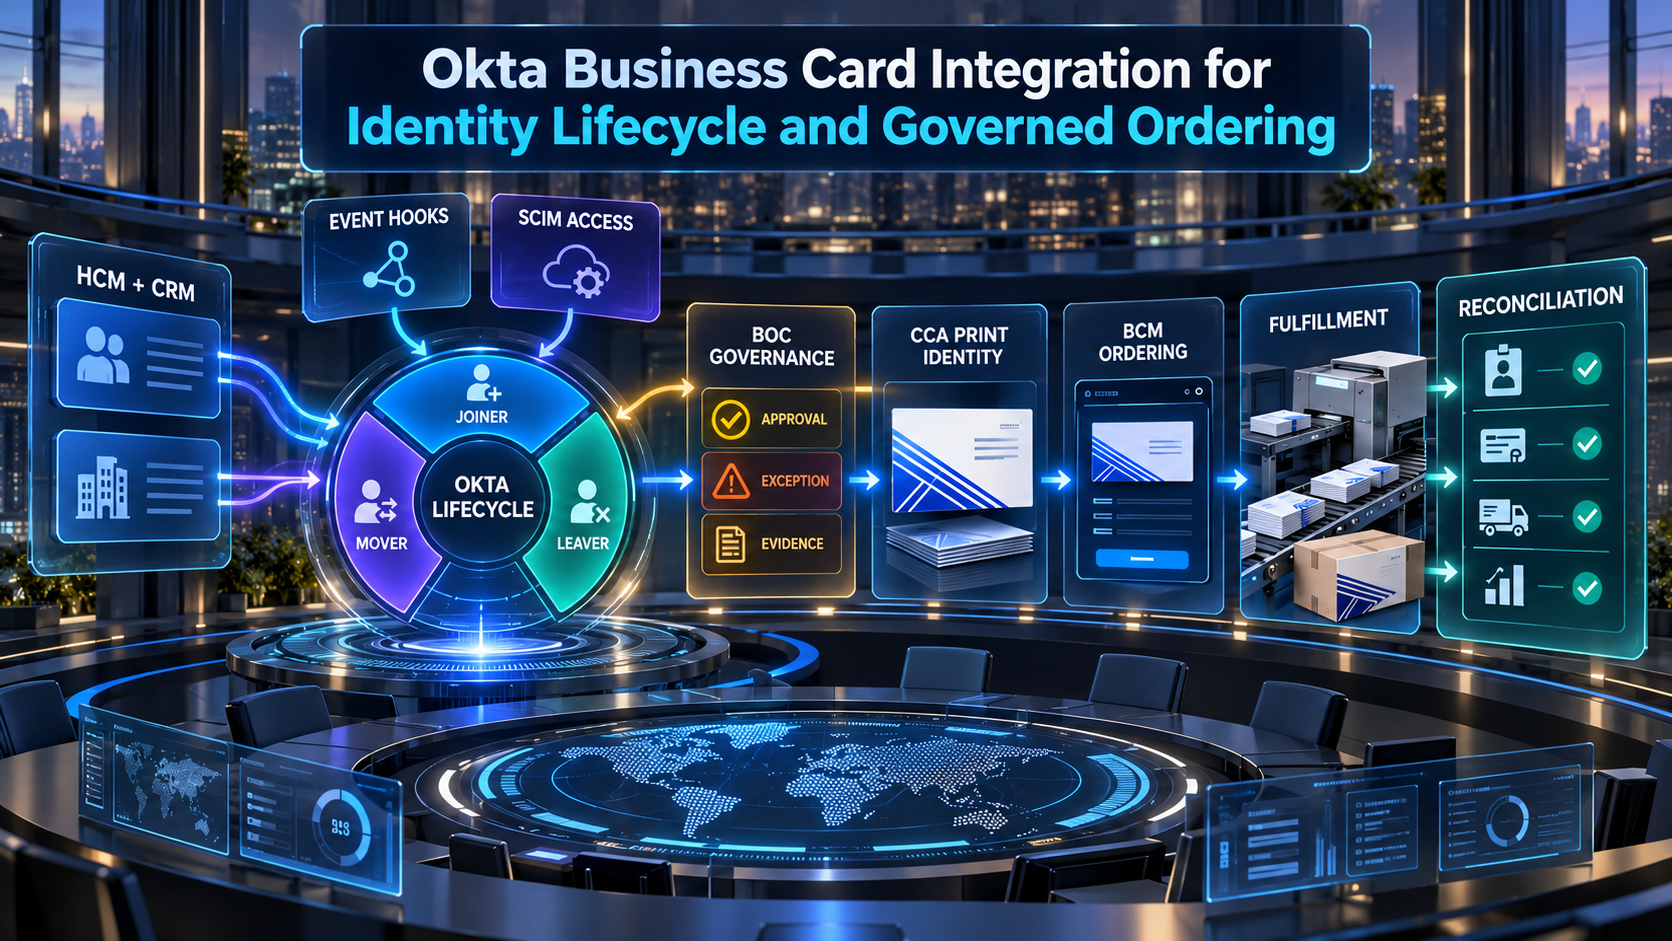
Connecting HCM and CRM context, Okta identity events, CCA identity governance, Business Card Manager ordering, fulfillment, and evidence through BOC.
Okta can govern digital identity lifecycle, application access, and provisioning signals, but it should not become the authority for public identity or business-card production. CCA governs the identity approved for print, Business Card Manager is the contracted business-card vendor and ordering system, and BOC controls the cross-system workflow, exceptions, reconciliation, and closure.
Identity Lifecycle Automation Needs a Business Outcome Layer
A user activation, profile update, group assignment or deactivation can indicate that an employee is joining, changing responsibilities or leaving. Those signals are valuable because they can reduce manual discovery. They do not establish that a person needs business card integration, that every profile field is suitable for external use or that a supplier order may be released.
Directly connecting an identity event to production can turn access administration into unintended purchasing authority. An Okta profile may contain an internal job title, a directory location or an email value that serves authentication and provisioning. The printed version may require different brand, legal, language, address, and disclosure rules.
Business Ops Center provides the operating layer between the signal and the outcome. It correlates HCM, CRM, and Okta context, qualifies demand, coordinates CCA and BCM, controls approvals and exceptions, and verifies delivery and financial evidence before closure.
Separate Workforce Access Print and Fulfillment Authority
HCM remains authoritative for configured workforce facts such as employment status, manager, organization, job, work assignment, location and effective dates. CRM can remain authoritative for customer-facing responsibility, territory, accounts, campaigns and events. These systems explain business need and timing.
Okta governs digital identity state, authentication relationships, groups, application assignments and provisioning within the configured organization. Profile sourcing can reflect creation, updates and terminations from an HR or directory source. Okta should not independently decide which internal values become public identity.
CCA governs printable identity, including the approved display name, external title, organization, office, phone, email, language, legal text, logo and template. Business Card Manager (BCM) is the contracted business-card vendor and ordering system. BCM manages products, proof, quantity, production, shipment, correction, cancellation and reorder state. BOC governs transitions across these authorities.
Okta Supports Several Configurable Integration Mechanisms
Okta documents lifecycle operations for users, profile sourcing from HR and directory systems, asynchronous Event Hooks, SCIM provisioning and Okta-Connected business identity workflows. Event Hooks send HTTPS REST calls when selected events occur. SCIM can create, update and deactivate users and groups in supported downstream applications.
An implementation may use Event Hooks, Okta Management APIs, SCIM, Okta Workflows, an integration platform, scheduled polling or reconciliation. The appropriate choice depends on subscriptions, organization configuration, event eligibility, profile ownership, security, data latency, supported interfaces and operational scale.
This article describes a configurable architecture, not a universal released connector among Okta, BOC, CCA and BCM. BOC adds business qualification, stable correlation, idempotency, versioned decisions, exception ownership and outcome reconciliation. Technical delivery alone does not prove that a card was correctly authorized and delivered.
The Governed Okta Business Card Lifecycle
| Lifecycle stage | Authoritative context | BOC control | Required outcome |
|---|---|---|---|
| Need | HCM or CRM event and effective date | Authenticate correlate and qualify demand | Trusted BOC case |
| Digital identity | Okta user state groups and permitted profile facts | Confirm readiness without granting print authority | Verified identity context |
| Printable identity | CCA policy and approved public fields | Resolve conflicts and preserve version | Approved card identity |
| Order | BCM product proof quantity and destination | Check policy duplication and authority | Controlled BCM order |
| Fulfillment | BCM production shipment and delivery | Monitor state and route exceptions | Verified physical outcome |
| Financial | Purchase receipt invoice credit and posting | Reconcile value and references | Supported financial outcome |
| Closure | Evidence current state and residual obligations | Authorize closure or assign remaining work | Auditable closed case |
Begin With an Authorized Business Need
The strongest trigger normally begins with HCM, CRM or an approved operational request. A customer-facing new hire may need cards before the first meeting. A role change may require a replacement. A conference assignment may justify a time-bound quantity even when no identity attribute changes.
BOC creates one case under a stable worker and requests a reference. Okta can confirm that the expected digital identity exists, has reached an appropriate lifecycle state, and has the application access required for the process. It should not convert every activation, import, profile update or group change into an order.
The trigger contract defines source, event type, changed properties, effective time, correlation keys, retry behavior, and ownership. BOC classifies the event as new demand, replacement, correction, cancellation, future action or no action and records the reason.
Treat Event Hooks as Signals Rather Than Instructions
Okta Event Hooks are asynchronous outbound calls that can trigger processing in external systems. Their event payloads provide useful context, but the receiving service must verify the request, interpret the event, and retrieve current permitted state when necessary. The Okta process does not wait for the external business outcome.
BOC records the event identity, time, source and target references, then checks whether the event is relevant to an open or potential card case. Repeated or out-of-order delivery must not create duplicate demand. An activation followed by a corrected profile should result in one governed state, not multiple orders.
Filters can reduce noise for supported event types, but filtering is not a substitute for policy. BOC still evaluates employment, customer-facing need, timing, prior orders, identity readiness, quantity, delivery and cost conditions before the workflow proceeds.
Profile Sourcing Requires Explicit Attribute Ownership
Okta profile sourcing can reflect user creation, updates and termination from third-party directory and HR applications. That makes source precedence and attribute mapping critical. The integration must document which system owns each field, how conflicts are resolved and which values may flow downstream. A value sourced into Okta is not automatically approved for print. The internal job classification may differ from an external title. A location code may not be a public office address. BOC passes only permitted candidate facts to CCA and preserves their source and effective time.
Business card ordering does not need passwords, authentication factors, sign-in history, sensitive group membership or unrelated profile data. The data contract should minimize fields, restrict service identities, mask logs and separate durable evidence from temporary integration payloads.
CCA Converts Permitted Context Into Printable Identity
CCA applies brand, legal, regional and identity rules to determine the public representation that can appear on the card. It can normalize names, titles, company names, addresses, contact formats, languages, credentials, disclaimers, logos and templates without rewriting HCM, CRM or Okta. The CCA result is versioned and linked to the BOC case. If employee status, role, company, office, email or phone changes after approval, BOC decides whether the request can continue, must hold or requires a replacement approval. A superseded version remains available for evidence but cannot silently authorize new production.
Exceptions go to the owner of the decision: HR for workforce status, sales operations for customer-facing need, brand for printed representation, identity administrators for Okta state and procurement for commercial authority. BOC keeps the correction attached to the same case.
Business Card Manager Executes the Contracted Order
After BOC verifies current authority, BCM converts the approved CCA identity into the contracted card product. It manages product configuration, artwork rendering, proof, quantity, production, shipment, delivery, correction, cancellation and reorder state. BCM does not select another vendor or decide employee eligibility. Standard orders may proceed automatically when product, quantity, delivery, timing and cost rules are satisfied. Rush service, unusual quantities, nonstandard finishes, new delivery destinations or repeated reorders can require additional approval. BOC records the rule and evidence for each decision.
The BCM order and line identifiers remain linked to the Okta user reference, HCM worker, CRM context, BOC case, CCA version, purchase document, shipment and invoice. This correlation supports investigation without copying excessive personal data into every system.
Joiner, Mover, and Leaver Scenarios Need Different Policies
For a joiner, Okta activation can be one readiness condition alongside an accepted HCM hire, effective start date, work email, customer-facing role, CCA approval, manager decision, delivery address and purchasing authority. Preparation may begin early, but production should wait until required facts stabilize. For a mover, BOC compares the new state with the last approved and produced identity. An application assignment or group change may require no card action. A customer-facing promotion, organization change, office move or new email domain may justify replacement and cancellation of stale work.
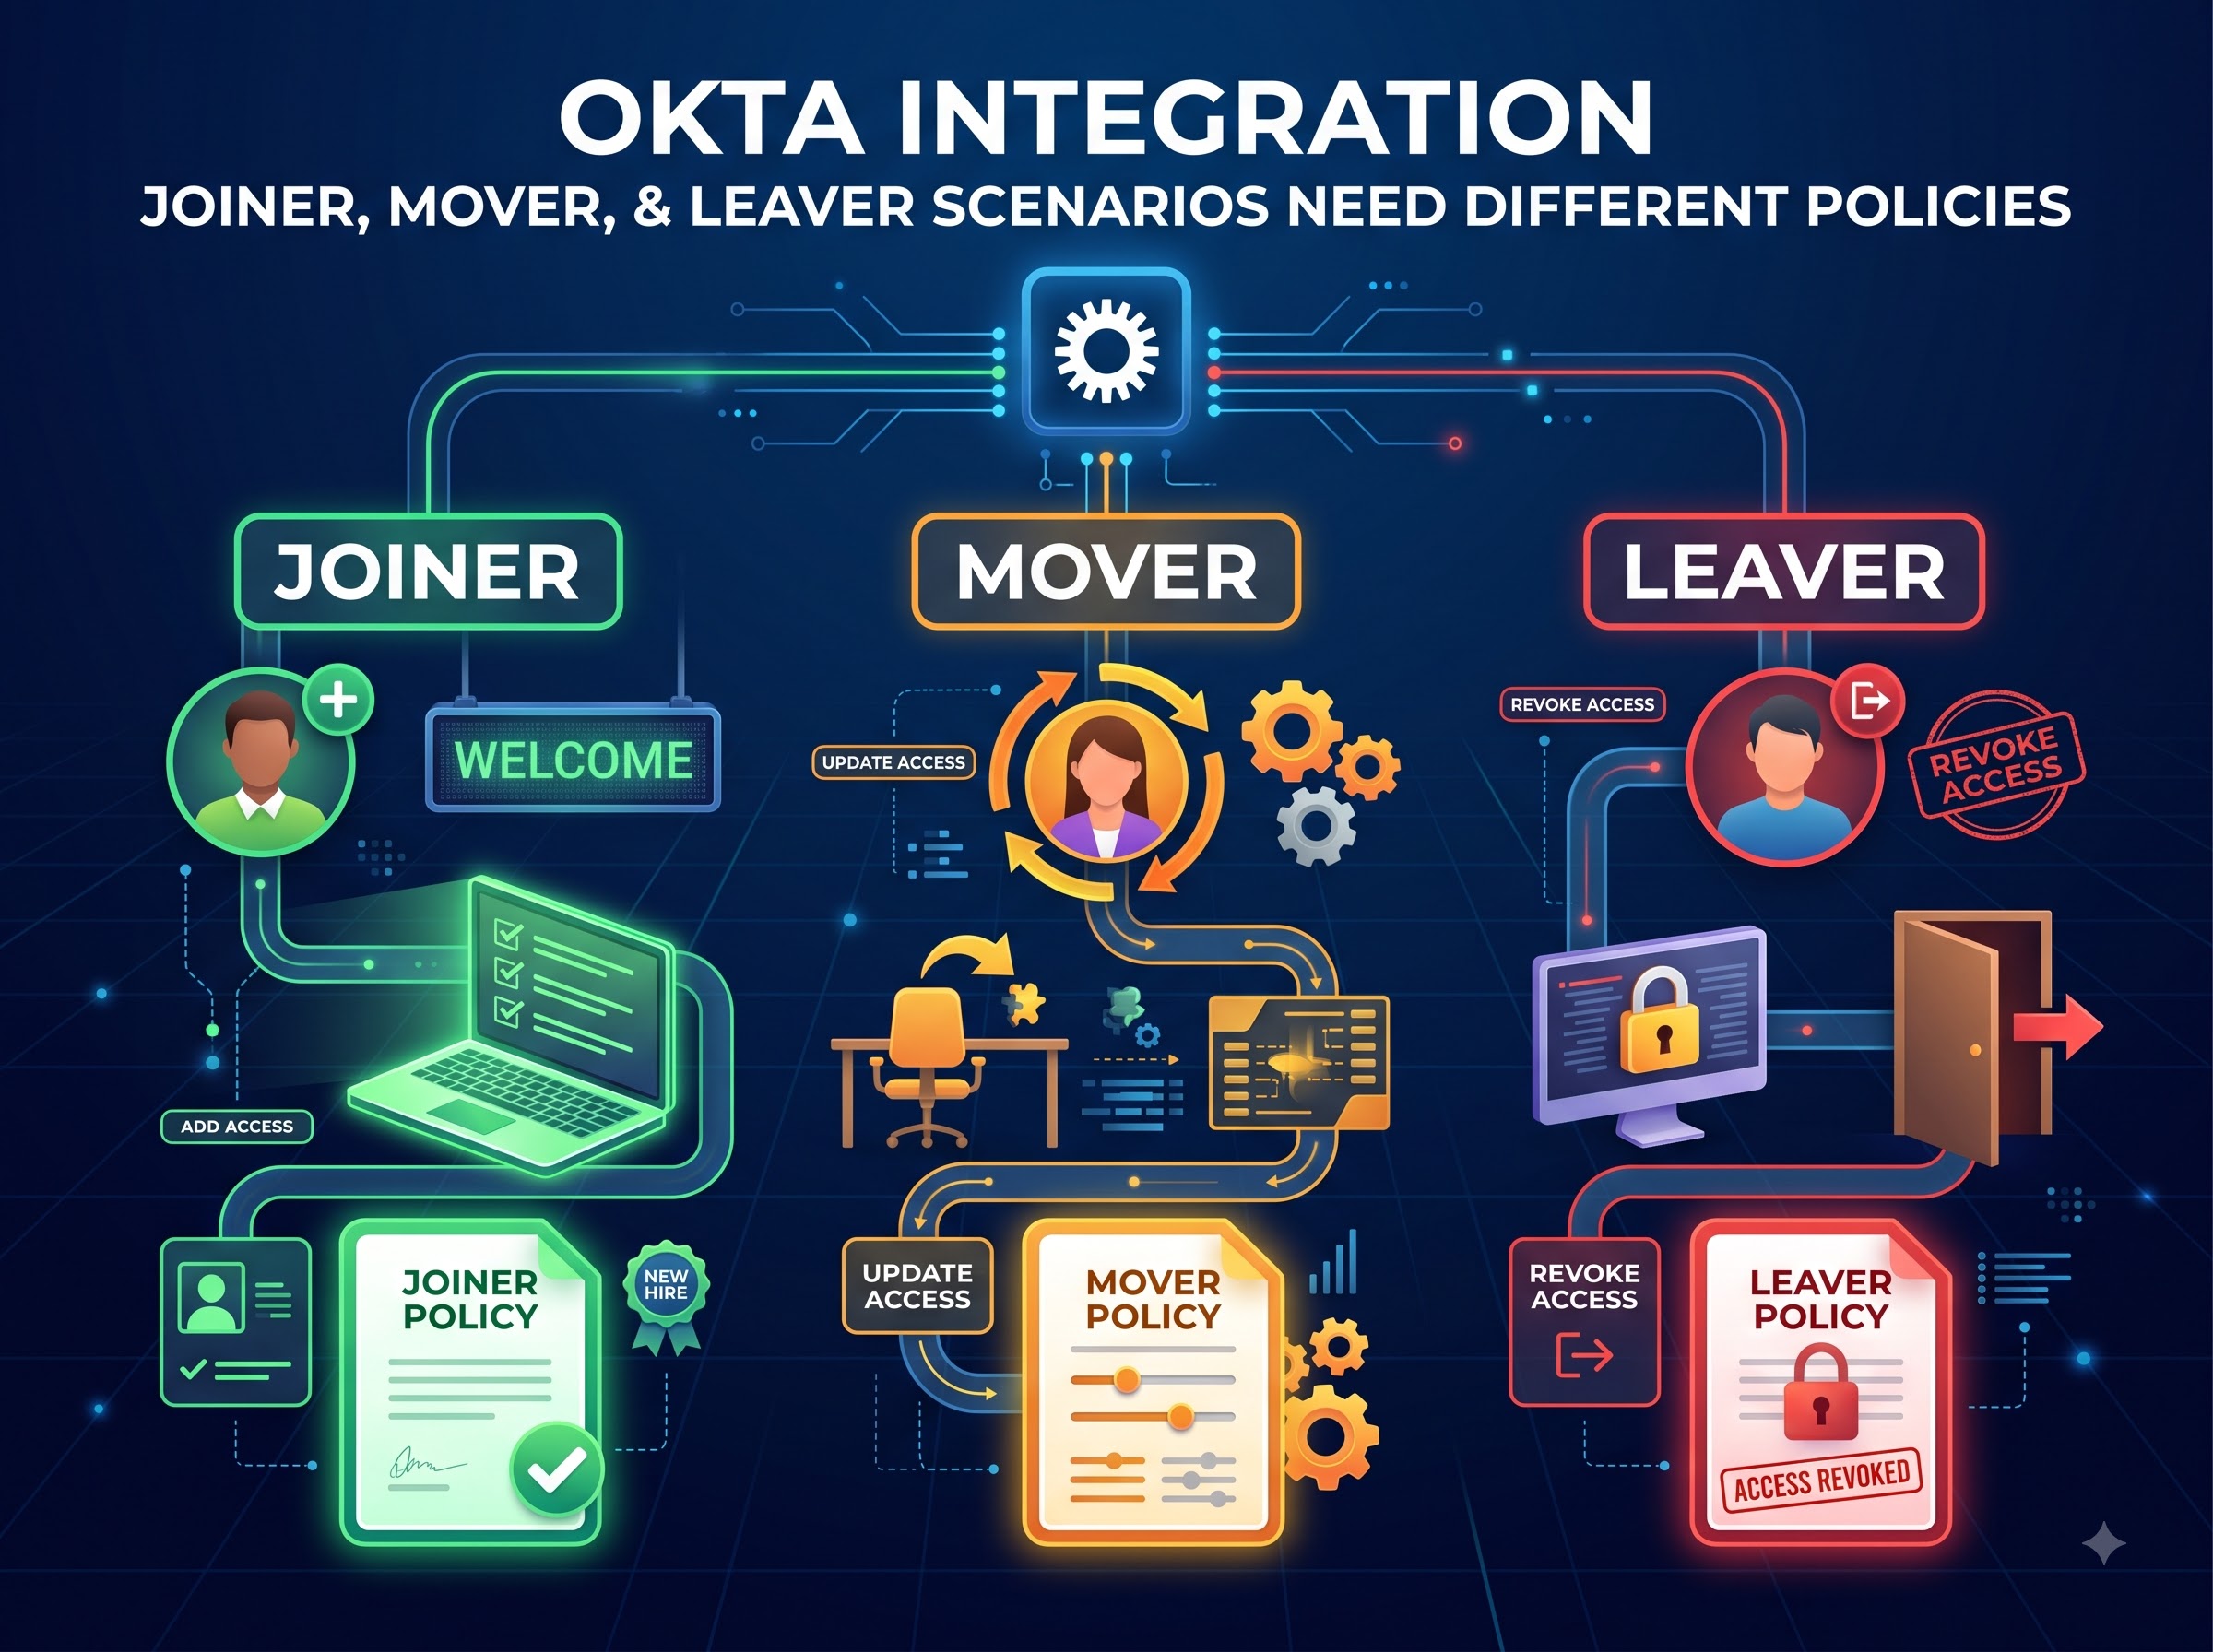
For a leaver, Okta deactivation can stop future access and ordering authority. It does not erase a card already produced, a shipment in transit or an invoice awaiting treatment. BOC attempts cancellation where possible, prevents reorders and records unavoidable cost and residual obligations.
SCIM Provisioning Is an Access Boundary Not Print Approval
SCIM standardizes provisioning between Okta and applications. Where a supported and approved SCIM integration exists, Okta can create, update or deactivate the application identity used to request, review or administer business cards. This can reduce manual access administration. Provisioning a person into BOC, CCA or BCM should not create an order. Application access, card eligibility, approval authority and production release are separate decisions. BOC evaluates current role and policy at the moment of action rather than assuming that an account assignment permanently grants authority.
SCIM design must define matching attributes, uniqueness, mappings, create and update behavior, deactivation, group handling, error quarantine and recovery. Unsupported protocol features and product-specific behavior must be validated against the deployed Okta environment and downstream service.
Okta Workflows Can Coordinate Tasks Without Replacing BOC
Okta Workflows can respond to events, call connected applications and run configurable flows. It can be useful for identity-adjacent automation, data transformation and targeted calls. BOC remains responsible for the governed business case, cross-system decisions, exceptions, evidence and closure. A workflow that invokes BOC should pass a stable event reference and the minimum permitted context. BOC returns a case or processing result that can be monitored without placing complete business-card payloads in identity-flow history. Failure handling must distinguish retryable technical issues from business exceptions.
This division prevents identity automation from becoming a second ordering-policy engine. Okta manages digital identity operations; BOC manages the enterprise outcome; CCA and BCM retain their defined identity and fulfillment responsibilities.
Secure Hooks APIs and Provisioning With Least Privilege
Okta API tokens, OAuth clients, service applications, event-hook endpoints, SCIM credentials and workflow connections require named ownership and controlled storage. Use the narrowest supported permissions, environment separation, rotation, monitoring and periodic access review. Event Hook endpoints should implement Okta verification and authenticate requests using a supported design. Processing should validate schema and event type, limit payload retention and avoid sensitive information in logs or tickets. Rate limits, timeouts, backoff and uncertain delivery require explicit recovery rules.
Every downstream service must enforce its own authorization. A message from Okta does not override CCA policy, BCM ordering controls, procurement approval or BOC case state. Material transitions should be attributable to an authenticated actor, workload or approved automated rule.
Reconciliation Finds What Event Processing Misses
Asynchronous systems can produce repeated, delayed or missed work. Scheduled reconciliation compares expected HCM or CRM changes, Okta lifecycle state, open BOC cases, CCA decisions and BCM orders. It can reveal unprocessed joiners, stale approvals, duplicated demand, disabled users with open orders and orphaned fulfillment. Technical reconciliation confirms that hooks, APIs, SCIM and workflows processed. Operational reconciliation confirms that the approved card reached the correct destination. Financial reconciliation compares purchase, receipt, invoice, freight, tax, credit and reprint activity with the authorized BCM order.
BOC closes the case only when the current identity and eligibility state, physical delivery and financial outcome agree or a named authority accepts the remaining exception. This avoids declaring success because one API request returned a successful status.
Implement One Identity Journey Before Expanding
Begin with one Okta organization, one workforce population, one joiner or mover scenario, one CCA policy, one BCM product and one delivery path. Map the current manual process, source ownership, minimum data, profile mappings, events, approvals, exceptions, evidence and retention before development.
Confirm lifecycle states, event-hook eligibility, payloads, verification, API permissions, SCIM capabilities, workflow connections, rate limits and monitoring for the selected environment. Define the BOC case key, CCA version, BCM order reference, retry behavior, reconciliation schedule and support owners.
Test pre-hire activation, delayed start, duplicate hook, out-of-order profile update, missing email, title conflict, group change, mover, deactivation, rehire, mapping error, permission failure, hook outage, uncertain order acceptance, proof rejection, partial delivery, invoice variance, credit and reprint.
Buyer Intent Bridge What an Okta Integration Engagement Produces
Organizations do not need another profile export. They need an operating contract across workforce context, digital identity, public identity, contracted ordering, purchasing, fulfillment and finance. A BOC engagement can produce the source-of-truth matrix, event catalogue, data contract, permission model, lifecycle design, approval rules, exception taxonomy and reconciliation plan.
The architecture protects existing investments. HCM and CRM retain their domain authority. Okta governs digital identity and application access. CCA governs printable identity. Business Card Manager remains the contracted business-card vendor and ordering system. BOC governs transitions, evidence and accountable closure.
Start with a manual handoff that causes delay or correction, such as customer-facing new-hire cards or replacements after role changes. A focused implementation creates a visible result and a reusable pattern for other identity-linked business operations.
Questions Integration Buyers Should Ask
- Which HCM or CRM event establishes business need, and which Okta lifecycle state is required?
- Which Event Hooks, Management APIs, SCIM capabilities, or Okta Workflows are approved for the organization?
- Which profile attributes may be used for correlation, which may be printed, and which are prohibited?
- How are the worker, Okta user, BOC case, CCA version, BCM order, shipment, purchase, and invoice correlated?
- How are duplicate, delayed, missed, and out-of-order events detected and recovered?
- Who owns credentials, mappings, hooks, monitoring, exceptions, reconciliation, retention, and support?
Frequently Asked Questions
Does BOC replace Okta? No. Okta remains the digital identity and access platform. BOC governs the cross-system business workflow, evidence and verified outcome.
Does Okta activation automatically create a business card order? No. It is one signal that BOC can evaluate with HCM, CRM, CCA, procurement and policy context.
Is a universal native connector claimed? No. This article describes a configurable architecture using customer-approved Okta and downstream capabilities.
What is Business Card Manager? Business Card Manager is the contracted business-card vendor and ordering system that manages configured products, proof, production, fulfillment and reorders.
Connect one Okta identity lifecycle to a governed business card outcome. Business Ops Center can define the authority model, event and provisioning architecture, CCA identity approval, BCM ordering, exception handling and reconciliation required for a controlled implementation. Start with one high-friction joiner or mover path and turn it into a reusable integration pattern.